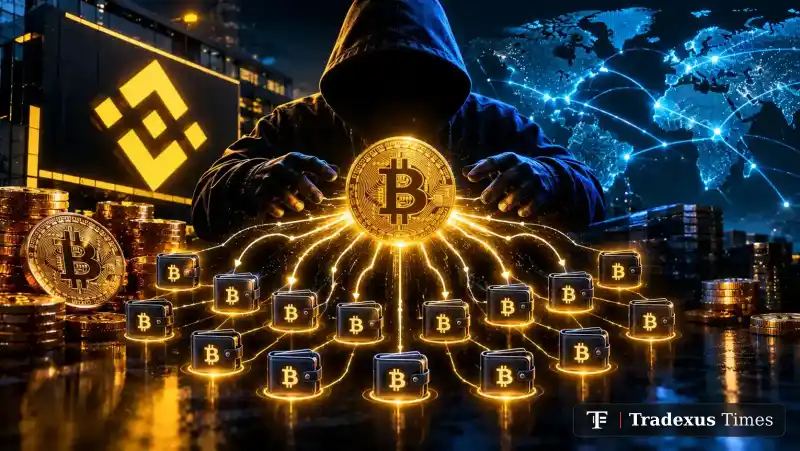
The attacker behind the $1.4 billion Binance Bitcoin theft has distributed 18,270 BTC across 19 separate wallets, completing the transfers within minutes of receiving the stolen funds. The coins have remained untouched since the redistribution, creating a significant challenge for recovery efforts.
The initial transfers took place at 20:20 UTC, when Binance's hot wallet sent more than 18,270 BTC to a single destination through 11 transactions, all confirmed in the same Bitcoin block. The attacker then used a technique known as a peel chain, gradually separating approximately 1,000 BTC into fresh addresses while forwarding the remaining balance through successive transactions.
In this story
2 assets

The resulting distribution left 17 wallets holding exactly 1,000 BTC each, another containing 832.5 BTC, and a final address holding 437.7 BTC. None of the 19 wallets had transferred any bitcoin as of 04:23 UTC on Friday. The only subsequent activity involved small unsolicited deposits sent by unrelated wallet addresses.
Bitcoin's decentralized structure makes the situation particularly difficult to contain. Unlike centralized stablecoin issuers such as Tether, Circle, and Ripple, which can blacklist addresses through their token contracts, Bitcoin has no central authority capable of freezing individual holdings. Consequently, restricting access to the stolen funds largely depends on identifying and intercepting them if they reach exchanges, over-the-counter trading desks, or swap services.
TRM Labs attributed the attack to North Korea-linked hacking group TraderTraitor with high confidence. The attribution adds a broader security dimension to the incident, particularly given the group's previous involvement in the $1.5 billion Bybit theft in February 2025. Following that attack, the group reportedly spent approximately 10 days converting stolen Ether into Bitcoin.
The structure of the Binance withdrawals also provides important clues about how the breach was executed. Each of the 11 transactions resembled a standard exchange withdrawal, with valid signatures generated by Binance-controlled Bitcoin addresses. In one transaction, multiple Bitcoin inputs were consolidated, with the remaining change returned to Binance.
Binance's initial investigation indicated that the attacker may have gained access through a compromised laptop belonging to a DevOps engineer. The device reportedly provided access to a service container that was subsequently used to submit unauthorized withdrawal requests. Binance stated that investigators had found no evidence of a private-key leak, suggesting the incident may have involved compromised operational access rather than a direct breach of wallet cryptographic keys.
For the broader cryptocurrency market, the incident highlights the distinction between blockchain transparency and the ability to recover stolen assets. Although Bitcoin transactions can be tracked publicly, identifying the movement of funds does not automatically provide a mechanism to freeze them. The immediate focus will therefore remain on whether the attacker attempts to consolidate, exchange, or move the bitcoin through services capable of restricting access.