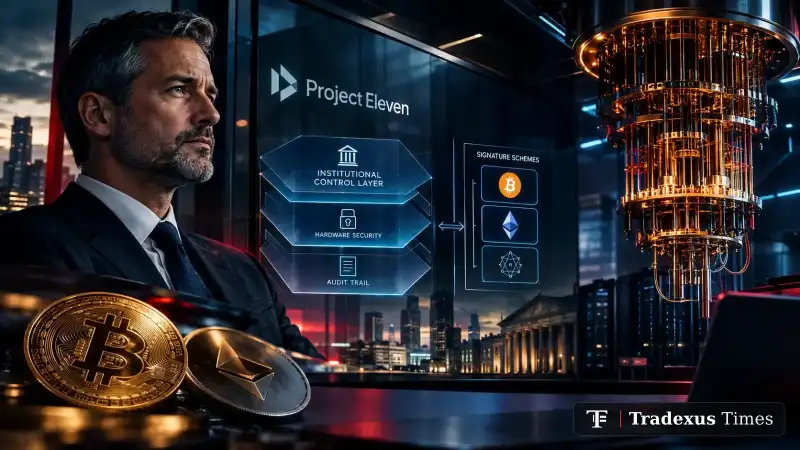
Institutional crypto custody firms are preparing for the possibility of a future quantum threat by building migration paths before blockchain networks face an emergency cryptographic transition. The challenge is particularly complex for institutions because custody systems must preserve approval controls, hardware-based key storage and audit trails while potentially adapting to new signature schemes.
Project Eleven’s Strongpoint custody platform is designed to separate the institutional control layer from the signature scheme used by an underlying blockchain. This architecture could allow custodians to maintain their existing approval and security infrastructure while supporting different cryptographic standards as blockchain protocols evolve.

“Strongpoint isn’t a replacement for protocol-level adoption of post-quantum cryptography,” Pruden said. “But the decoupled architecture allows us to support protocols in an agile manner.” The approach reflects a broader effort to prepare institutional custody infrastructure before a quantum-capable system creates pressure for rapid migration.
Quantus is taking a different approach at the cryptographic layer, using ML-DSA for key generation and transaction signatures. ML-DSA is a post-quantum signature standard selected by the U.S. National Institute of Standards and Technology, positioning the technology as a direct response to the potential security implications of future quantum computing.
Smith said institutions should view a surprise advance in quantum computing as a portfolio risk rather than solely a technology problem. For digital-asset holders, the issue is centered on the potential exposure of wallet keys, while institutions must also consider how their broader custody and transaction-authorization infrastructure would function during a cryptographic transition.
The timing of quantum computers capable of attacking Bitcoin or Ether remains uncertain, but the potential response would require broad agreement among developers and users. That governance requirement makes preparation outside the blockchain particularly important, because a network-level migration could take time even after a credible threat becomes apparent.
For institutional investors and custody providers, the key issue is therefore not whether a quantum attack is imminent, but whether their infrastructure can adapt without forcing an emergency migration. The development of decoupled custody architectures and post-quantum signing systems suggests that institutions are increasingly treating cryptographic resilience as part of long-term portfolio and operational risk management.